

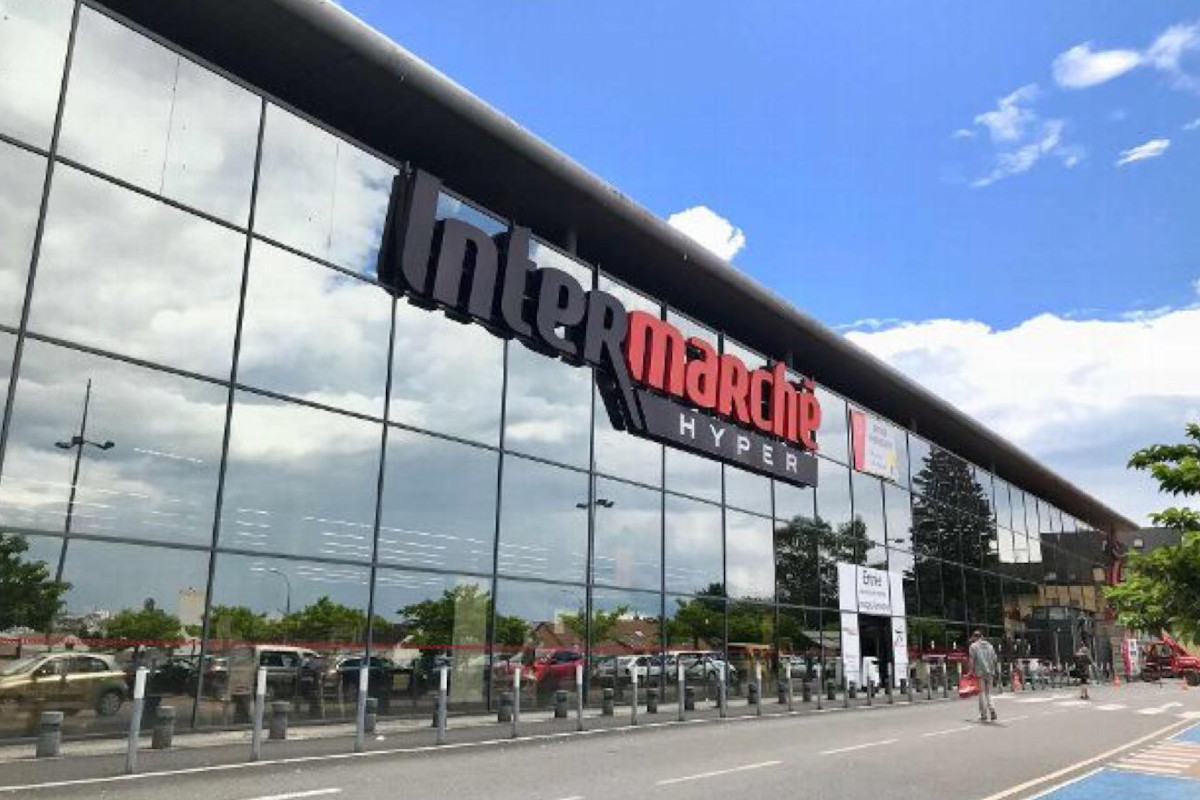
French supermarket giant Intermarché has been forced to throw away fresh and frozen food after hackers remotely raised the temperature of refrigeration systems to 50C, in a cyberattack that has affected hundreds of stores across France.
Around 150 Intermarché supermarkets were hit, with fridges and freezers running at the unusually high temperature for six hours overnight, leaving food unfit for sale.
The attack has also affected rival grocers Carrefour, Monoprix and Coopérative U, with some stores reporting fires as well as substantial food losses.
Carrefour confirmed that 80 of its supermarkets had been affected, while Monoprix said around five per cent of its 490 stores had been targeted.
Intermarché owner Les Mousquetaires said all food affected by the incident had been discarded to avoid putting customers at risk.
Speaking to French broadcaster BFM TV, Intermarché boss Thierry Cotillard described the attack as unprecedented, estimating that losses across the French supermarket sector could run into tens of millions of euros in a single day.
The scale of the disruption has prompted French Prime Minister Sébastien Lecornu to order the country’s national cybersecurity agency, ANSSI, to investigate.
The Paris prosecutor’s office has also launched an investigation, while French authorities are working with European counterparts amid concerns that retailers in other countries may have been targeted.
Unlike cyberattacks that compromise customer data or take down online shopping platforms, this incident targeted the refrigeration equipment that supermarkets rely on to keep food safe.
Modern refrigeration systems can be managed remotely, allowing maintenance companies to adjust temperatures and monitor equipment without visiting individual stores.
It is that connectivity which appears to have left hundreds of supermarkets exposed.
French authorities identified a vulnerability involving refrigeration management software supplied by Danish engineering group Danfoss.
The company acknowledged incidents involving its systems in France and said the affected equipment had been running outdated firmware.
It added that customers had long been advised to install the latest software updates and replace older equipment with newer systems.
Cybersecurity researchers at Claroty had previously identified vulnerabilities in a Danfoss refrigeration controller that could allow attackers to bypass authentication controls and execute code remotely. Danfoss subsequently issued software updates to address the flaws.
However, the precise method used in the latest attacks has not been publicly established.
The incident has raised concerns well beyond France, with cybersecurity researchers reporting that similar attacks have affected retailers in Spain, Portugal, Poland, Germany and Belgium.
Dutch supermarket group Ahold Delhaize, which owns Albert Heijn and operates several major US grocery chains, has separately reported a security incident that forced it to take systems offline.
The disruption affected online grocery deliveries, although its physical stores remained open.
Ahold Delhaize said there was no reason to believe its incident was connected to the attacks in France.
Click here to sign up to Retail Gazette‘s free daily email newsletter