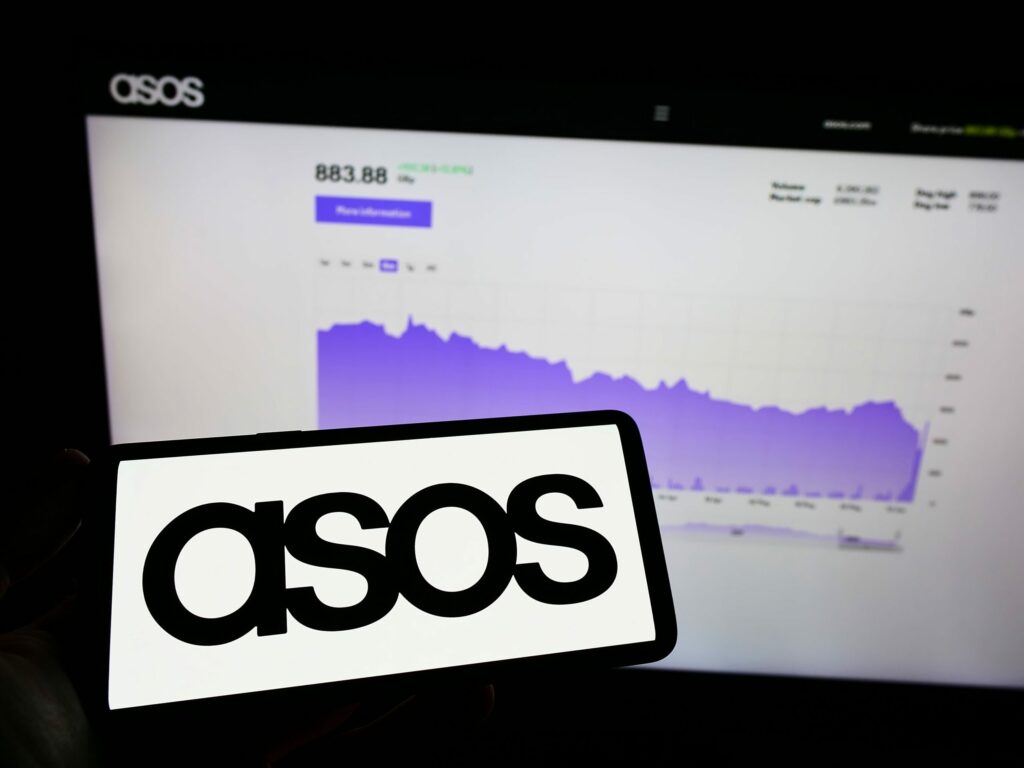


ASOS has stressed that it does not believe that payment-card information or account passwords were impacted in a hacker incident earlier today.
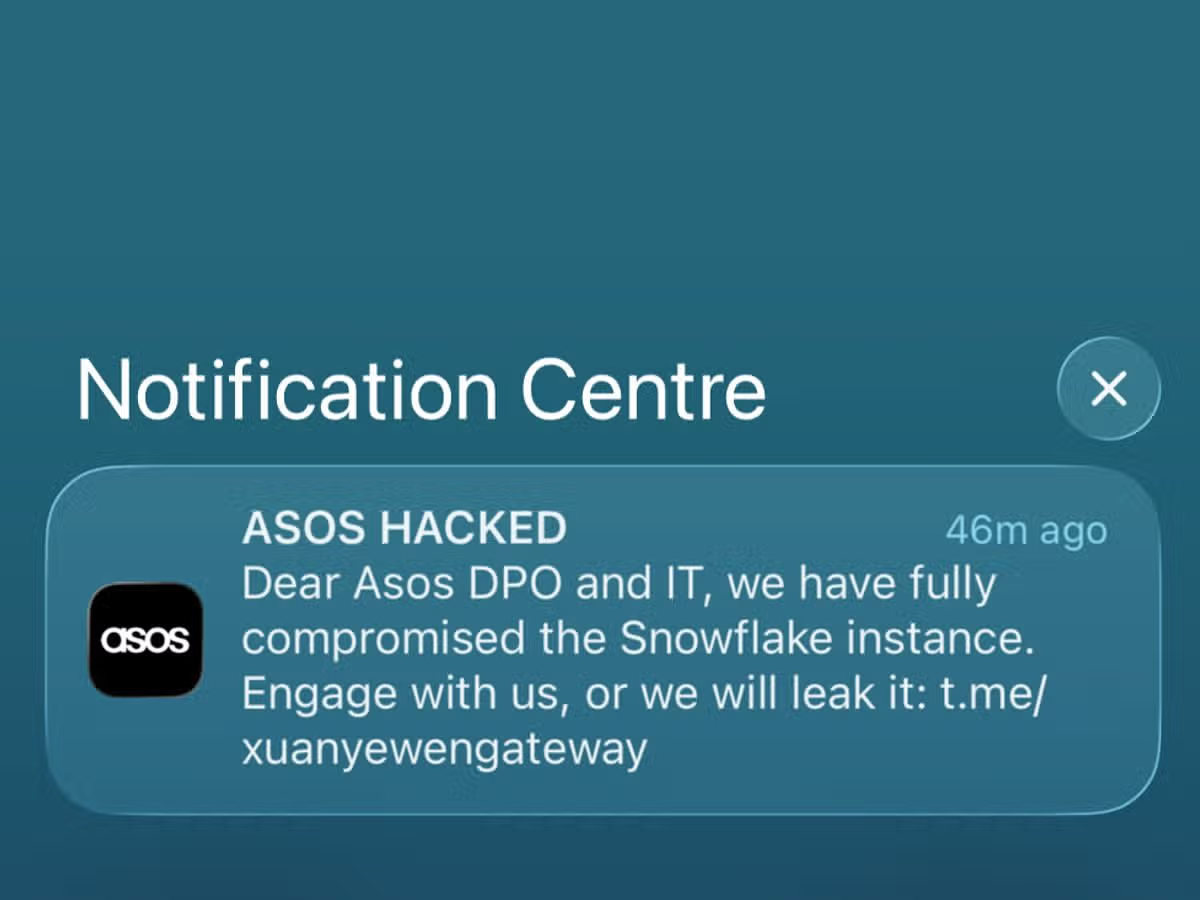
Following ASOS app users receieved threatening notifications, the digital fashion platform admitted that basic personal information including name and contact details may have been accessed.
In a statement, to the London Stock Exchange, ASOS said: “We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers. We took immediate action to restrict access to the notification platforms and are working with our internal and external specialist advisers, as well as all relevant authorities.”
The ASOS website and app are operating as normal, with no current disruption to any aspects of operations.
Related Story

“Customer trust is incredibly important to us, and if the situation changes an update will be provided as appropriate,” stressed ASOS.
“The company has cyber security insurance with a large global provider, including business continuity insurance. It is early to quantify any potential impact on trading.”
The message told ASOS’ data protection officer and IT team that they had “fully compromised the Snowflake instance” and threatened to leak information unless the company engaged with them.
The notification included a link to a newly created Telegram channel called the Xuanye group gateway and referred to Snowflake, a cloud data platform used by companies to store and manage data.
This resulted in shares plummeting 11 per cent in morning trading.
Click here to sign up to Retail Gazette‘s free daily email newsletter