Hobbs, Whistles and Phase Eight hit by cyber incident as retailers face fresh attacks

Hobbs
EcommerceNewsTechnology

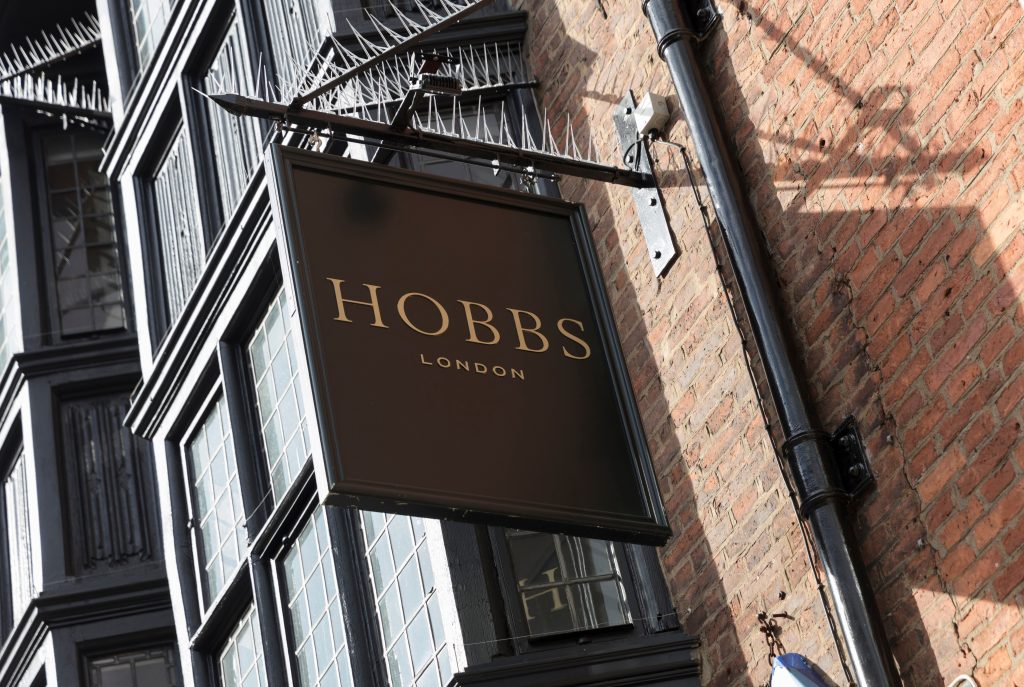
Hobbs, Whistles and Phase Eight have been hit by a cyber incident that has left several IT systems unavailable, just days after Asos became the latest major fashion retailer to fall victim to hackers.

The three fashion chains, owned by South African retail group The Foschini Group, were affected by an incident identified on Sunday, prompting the business to bring in external cybersecurity specialists.

TFG said it had activated its incident response and business continuity plans and reported the matter to the relevant UK authorities.

Stores remain open and trading, although several IT systems are still unavailable as the company works to contain the incident.

TFG is also investigating whether any personal or sensitive information has been compromised, with the full extent of the breach yet to be established.

It confirmed that its other UK brands, White Stuff and Inside Story, have not been affected, while its operations in Africa and Australia remain unaffected because they run on separate systems.

The incident took place during another difficult week for retail cybersecurity, following an attack on Asos that saw hackers gain access to customer information and send threatening notifications directly through its app.

Last Tuesday, Asos customers received a message claiming the business had been hacked and warning that stolen information could be released.

The online retailer subsequently confirmed that an unauthorised party had accessed an employee’s account by impersonating a trusted contact to obtain login credentials.

Those details were then used to access information held on third-party platforms, including customer names and contact details, although Asos said payment card information and passwords had not been compromised.

ASOS insisted its website and app remained safe to use throughout the incident.

Meanwhile, H&M is investigating claims that it has also been targeted by hackers. There is currently no evidence linking the incidents involving TFG, Asos and H&M.

The latest attacks follow a particularly damaging period for British retailers, with Marks & Spencer and the Co-op both suffering major breaches last year.

M&S was forced to suspend online clothing orders for seven weeks following its April 2025 cyberattack, while disruption to stock availability and distribution continued long after its website resumed trading.

Its latest annual results laid bare the financial damage, with £131.3m in costs directly associated with the incident during its 2025/26 financial year.

Fashion, home and beauty sales fell 7.7 per cent over the period, with the company pointing to the impact of suspended online trading, disrupted stock flows and restricted product availability.

The Co-op also suffered considerable disruption following its own attack last April, which caused product shortages across stores and resulted in the personal information of all 6.5 million of its members being stolen.

The Asos incident demonstrated how access to a single employee account can expose information held across third-party platforms, while the disruption at M&S showed how quickly an attack can turn into a prolonged trading problem.

For TFG, the immediate priority is restoring its affected systems and establishing whether customer or employee information has been accessed.

The group has not disclosed the cause of the incident, who may be responsible or when it expects normal IT operations to resume.

It said it would provide further updates should there be any material developments.

Click here to sign up to Retail Gazette‘s free daily email newsletter

EcommerceNewsTechnology

Leave a Reply

Your email address will not be published. Required fields are marked *

Fill out this field
Fill out this field
Please enter a valid email address.

Hobbs, Whistles and Phase Eight hit by cyber incident as retailers face fresh attacks

Hobbs

Hobbs, Whistles and Phase Eight have been hit by a cyber incident that has left several IT systems unavailable, just days after Asos became the latest major fashion retailer to fall victim to hackers.

The three fashion chains, owned by South African retail group The Foschini Group, were affected by an incident identified on Sunday, prompting the business to bring in external cybersecurity specialists.

TFG said it had activated its incident response and business continuity plans and reported the matter to the relevant UK authorities.

Stores remain open and trading, although several IT systems are still unavailable as the company works to contain the incident.

TFG is also investigating whether any personal or sensitive information has been compromised, with the full extent of the breach yet to be established.

It confirmed that its other UK brands, White Stuff and Inside Story, have not been affected, while its operations in Africa and Australia remain unaffected because they run on separate systems.

The incident took place during another difficult week for retail cybersecurity, following an attack on Asos that saw hackers gain access to customer information and send threatening notifications directly through its app.

Last Tuesday, Asos customers received a message claiming the business had been hacked and warning that stolen information could be released.

The online retailer subsequently confirmed that an unauthorised party had accessed an employee’s account by impersonating a trusted contact to obtain login credentials.

Those details were then used to access information held on third-party platforms, including customer names and contact details, although Asos said payment card information and passwords had not been compromised.

ASOS insisted its website and app remained safe to use throughout the incident.

Meanwhile, H&M is investigating claims that it has also been targeted by hackers. There is currently no evidence linking the incidents involving TFG, Asos and H&M.

The latest attacks follow a particularly damaging period for British retailers, with Marks & Spencer and the Co-op both suffering major breaches last year.

M&S was forced to suspend online clothing orders for seven weeks following its April 2025 cyberattack, while disruption to stock availability and distribution continued long after its website resumed trading.

Its latest annual results laid bare the financial damage, with £131.3m in costs directly associated with the incident during its 2025/26 financial year.

Fashion, home and beauty sales fell 7.7 per cent over the period, with the company pointing to the impact of suspended online trading, disrupted stock flows and restricted product availability.

The Co-op also suffered considerable disruption following its own attack last April, which caused product shortages across stores and resulted in the personal information of all 6.5 million of its members being stolen.

The Asos incident demonstrated how access to a single employee account can expose information held across third-party platforms, while the disruption at M&S showed how quickly an attack can turn into a prolonged trading problem.

For TFG, the immediate priority is restoring its affected systems and establishing whether customer or employee information has been accessed.

The group has not disclosed the cause of the incident, who may be responsible or when it expects normal IT operations to resume.

It said it would provide further updates should there be any material developments.

Click here to sign up to Retail Gazette‘s free daily email newsletter

Social


SUBSCRIBE TO OUR DAILY NEWSLETTER

  • This field is for validation purposes and should be left unchanged.
EcommerceNewsTechnology

Leave a Reply

Your email address will not be published. Required fields are marked *

Fill out this field
Fill out this field
Please enter a valid email address.

RELATED STORIES

Latest Feature


Menu


Please enter the verification code sent to your email: