

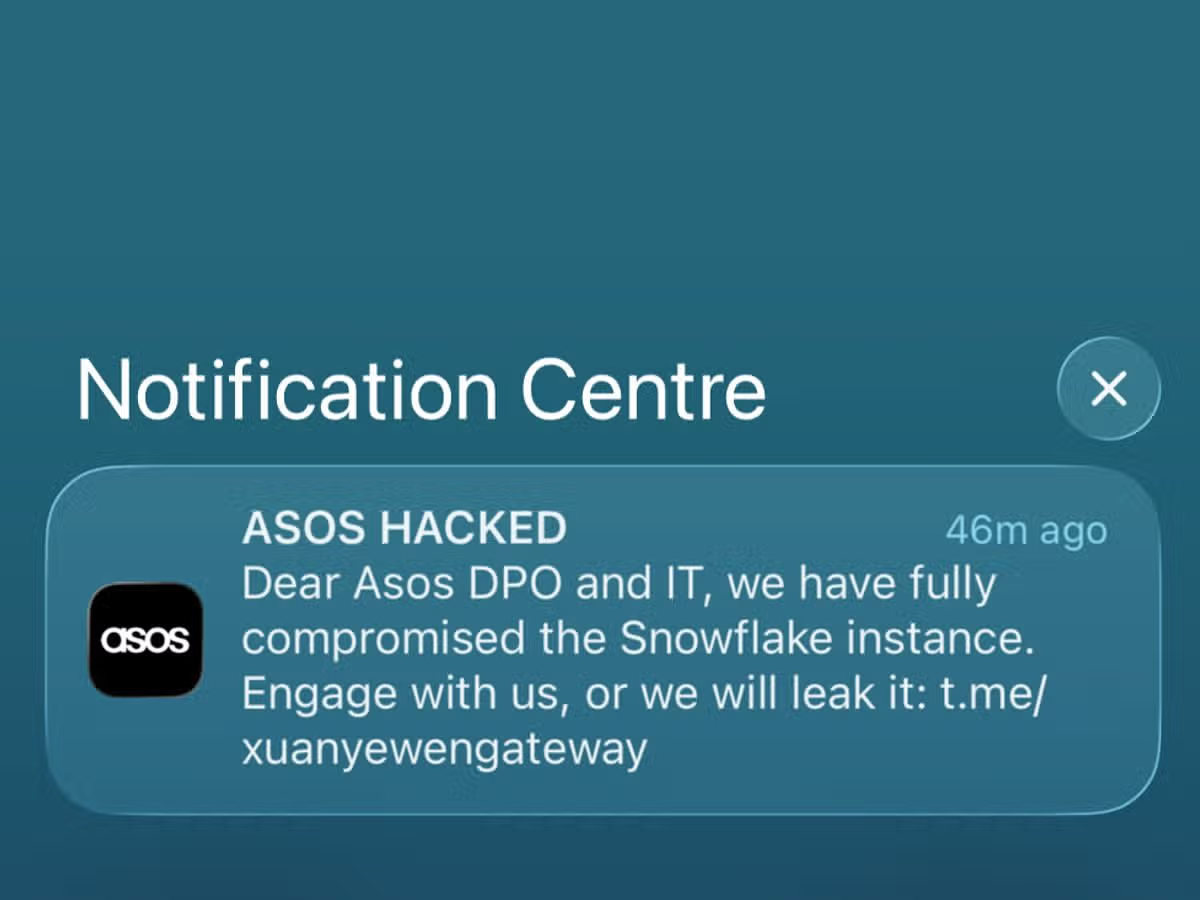
Digital fashion platform ASOS has provided its customers with an update following app users receiving threatening notifications on Tuesday morning, revealing that an unauthorised party gained access to an ASOS employee account.
The etailer has been conducting an investigation after it confirmed a cyber incident on 06 October 2026.
In a message to its customers, ASOS explained: “We discovered that an unauthorised party gained access to an ASOS employee account by impersonating a trusted contact to obtain log in credentials. Those credentials were then used to access information on certain third-party platforms used by ASOS.
“The affected platforms were immediately locked down, ensuring that no further information could be accessed and a full investigation was launched with the support of both internal and external cyber experts. We are also working with the relevant law enforcement and regulatory authorities.”
Related Story
ASOS had previously stressed that it did not believe that payment-card information or account passwords were impacted. They have now confirmed that.
The statement added: “Our investigation found that the unauthorised party had access to some personal information, including names and contact details, and certain non-personal account related information.”
It stressed the ASOS website and app were safe to use throughout, and remain safe to use today.
ASOS told its customers there is no action needed on accounts. But encouraged shoppers to remain cautious of unexpected messages or calls claiming to be from ASOS.
It said it would never ask for passwords, security codes or payment details through an unsolicited message or call.
ASOS concluded: “We know our customers trust us with their information. We take that responsibility seriously and have already taken additional steps to further strengthen security controls.”
Click here to sign up to Retail Gazette‘s free daily email newsletter